Text Us
HIPAA Compliant App Development Company

95%

Projects Delivered On Time

5★

Rating on Clutch

10+

Years of Experience

HL7&

FHIR Integration
Are You Building a Healthcare App Without Real HIPAA Safeguards?

Are You Building a Healthcare App Without Real HIPAA Safeguards?

Most teams treat HIPAA as a checklist they run the week before launch. By then the database schema, the APIs and the vendor list are fixed. Real HIPAA compliance mobile app development starts earlier and decides where PHI lives before anyone writes a single feature.

The average healthcare data breach cost $7.42 million in IBM's 2025 report. Many apps sold as HIPAA-ready still lack audit logs, signed BAAs or proper role-based access. Our HIPAA compliance app development solutions close those gaps before a regulator or an attacker ever finds them.

    HIPAA Compliant App Development Services by 8ration

    Our HIPAA compliant app development services cover patient apps, provider tools and the systems behind them. Each build starts with a map of where PHI enters, moves and rests, so security shapes every feature.

    HIPAA Compliant Mobile App Development

    HIPAA Compliant Mobile App Development

    We build iOS and Android apps that store, send and display PHI under strict controls. Data stays encrypted on the device and in transit. Sessions expire when idle and every access gets logged.

    arrow white

    Patient Portal Development

    Patient Portal Development

    Patients check lab results, book visits and message their care team through portals we build with identity checks, role-based permissions and full audit trails. Your staff members see only what their job requires.

    arrow white

    Telehealth App Development

    Telehealth App Development

    Our telehealth apps carry encrypted video visits, secure chat, prescriptions and scheduling. Every vendor in the call stack signs a BAA, and visit recordings stay locked to the care team that needs them.

    arrow white

    Healthcare Web App Development

    Healthcare Web App Development

    We build browser-based platforms for clinics, labs and payers with encrypted databases, hardened APIs and WCAG-aligned screens. Providers and administrators work from one secure system instead of juggling spreadsheets and long email threads.

    arrow white

    EHR/EMR Connected Apps

    EHR/EMR Connected Apps

    We connect your app to EHR and EMR systems through HL7 and FHIR interfaces. Records sync both ways with encryption, scoped tokens and logging, so clinicians see current data without entering it twice.

    arrow white

    HIPAA Compliance Audit & Gap Assessment

    HIPAA Compliance Audit & Gap Assessment

    For live apps we review the code, cloud setup and vendor contracts against the HIPAA Security Rule. You get a ranked list of gaps with a fix and an effort estimate for each.

    arrow white

    mHealth App Development

    mHealth App Development

    We build mobile health apps for remote monitoring, chronic care and wellness that pull readings from wearables and home devices. Data reaches your backend encrypted and opens only for clinicians with approved roles.

    arrow white

    Healthcare SaaS Development

    Healthcare SaaS Development

    We build multi-tenant healthcare SaaS where each customer's PHI sits in its own isolated space. Tenant-level encryption keys, access policies and audit logs give hospital buyers the clear answers their security reviews demand.

    arrow white

    Our Healthcare Work

    Health products test engineering discipline every single day they run. Our portfolio includes a patient access platform, a heart health tracker and a wellness app where a redesigned onboarding flow cut user drop-off by 40 percent.

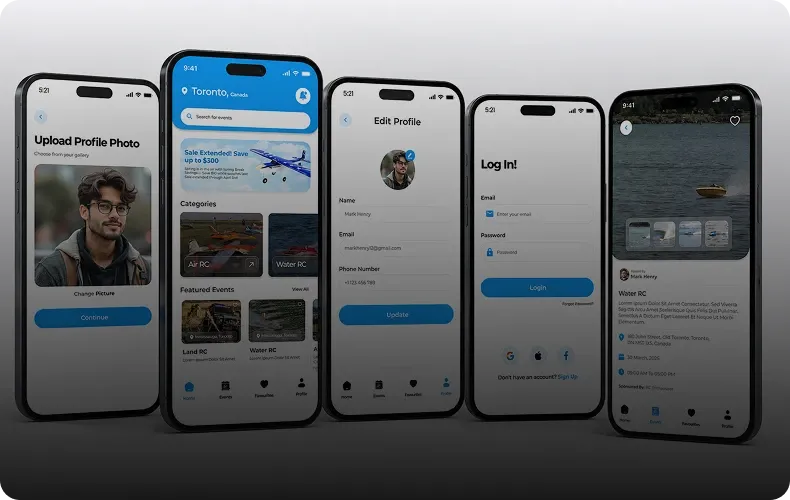
    RC Event Hub

    RC Event Hub

    RC Event Hub wanted to connect RC enthusiasts through events. We developed a platform that lets users discover, register, and track RC races easily in one place.

    Circle Track Connections

    Circle Track Connections

    Circle Track Connections wanted to help racing fans find love. We built a dating app that lets enthusiasts meet, connect, and form meaningful relationships.

    What's Built Into Every HIPAA Compliant App We Develop

    Every app we deliver carries one baseline of technical safeguards, whatever its size. That baseline drives our HIPAA compliance mobile app development, and we document each control so your security officer can show it to auditors.

    01

    End-to-End Encryption

    PHI is encrypted with AES-256 wherever it rests, including databases, device storage and backups. Data in motion travels over TLS 1.3, so intercepted traffic stays unreadable to anyone who lacks the keys.

    02

    Role-Based Access Control

    Each role reaches the minimum PHI its job requires. Billing staff work with billing data and clinicians work with clinical records. Admins change permissions in one place and the change applies everywhere.

    03

    Multi-Factor Authentication

    Anyone who touches PHI signs in with a second factor such as an authenticator app, a hardware key or biometrics. A stolen password alone never opens a patient record in your app.

    04

    Comprehensive Audit Logging

    Every read, edit, export and deletion of PHI writes a timestamped entry recording who acted, what changed and when. Logs are immutable and stored outside the app so nobody can alter them.

    05

    Secure API Architecture

    Our APIs authenticate every request, encrypt every payload and validate input before it reaches the database. Rate limits and scoped tokens stop a compromised client from pulling records it should never see.

    06

    Automatic Session Timeout

    Idle sessions close on their own after a period you set for each role. A phone left on a waiting room chair or an unlocked clinic workstation will not expose patient data.

    07

    HIPAA-Compliant Cloud Infrastructure

    We deploy on AWS, Google Cloud or Azure using HIPAA-eligible services only. Signed BAAs, private networks, encrypted storage and logging are switched on from the first environment we create for your project.

    08

    BAA Management

    Every vendor that stores or processes PHI needs a signed BAA. We identify each one, including hosting, email and analytics providers, collect the BAAs and keep the chain current as vendors change.

    09

    PHI Workflow Mapping

    Before any code exists we trace where PHI enters your app, where it moves and where it rests. That map decides the schema, the API design and every access rule we write.

    Why Choose 8ration as Your HIPAA App Development Company

    A HIPAA app development partner should leave you with a secure product and the paperwork to prove it. We work to ISO 27001 and ISO 9001 standards and hand over the documentation your auditors can follow.

    1.

    PHI-First, Not Compliance-Last

    −

    We map PHI workflows before we design architecture. Encryption, access rules and logging shape the first sprint. They never arrive as patches after launch, when changes cost more and risk breaking something.

    2.

    Full-Stack Healthcare Expertise

    +

    One team covers mobile, web, cloud, APIs and EHR integrations. Senior engineers lead from scoping to handoff, so the people who plan your compliance controls are the same people who build them.

    3.

    BAA-Backed Vendor Chain

    +

    Your app is exposed through every vendor it touches. We vet hosting, messaging, analytics and authentication providers, secure a signed BAA from each one and record the chain for your compliance files.

    4.

    Transparent Documentation

    +

    You receive the security architecture, data flow diagrams, risk assessment and audit log setup with the code. When a hospital or auditor asks how PHI is protected, your answer is already written.

    5.

    Post-Launch Security Support

    +

    We keep watching after release. Our team applies security patches, reviews access logs, updates dependencies and runs a yearly risk assessment so your safeguards keep pace with new threats and new features.

    6.

    Startup to Enterprise

    +

    We build HIPAA compliant MVPs from about $30K and enterprise platforms that run past $300K. The safeguards stay the same at every budget. Scope, integrations and scale are what change between them.

    Why Choose 8ration as Your HIPAA App Development Company

    Recognition We've Earned

    Healthcare buyers read reviews before they hand over a single patient record. Clients rate our work on Clutch, GoodFirms, DesignRush and Trustpilot, and we hold ISO 27001 and ISO 9001 certification for information security and quality.
    Clutch
    Techreviewer
    active

    Our HIPAA Compliant App Development Process

    Our HIPAA compliant application development services follow six clear stages with fixed checkpoints. You see every deliverable, approve each compliance decision and know at every step which safeguards are already in place and working.

    01

    PHI Discovery & Risk Assessment

    We map every PHI touchpoint, data flow, user role, third-party integration and cloud exposure. The risk assessment that comes out of this work sets the security requirements for everything we build next.

    02

    Secure Architecture Design

    We design the database schema, API structure and cloud infrastructure around HIPAA safeguards first. Features then fit into that structure, so later changes never open gaps in the protection around your PHI.

    03

    BAA Vendor Selection & Setup

    We list every vendor that will touch PHI, confirm each one offers a BAA and get it signed. Then we configure HIPAA-eligible accounts so no unprotected service slips into your production setup.

    04

    Secure Development (SDLC)

    Developers follow secure coding standards that cover RBAC, MFA, encryption, session controls and input validation. Every pull request goes through a code review with a security focus before it merges into main.

    05

    QA Testing & Compliance Validation

    We run vulnerability scans and penetration tests, verify access controls and review audit logs. Every finding gets fixed and retested, and you receive the compliance documentation that shows the app is ready.

    06

    Deployment & Ongoing Security Monitoring

    After launch we monitor the app, apply patches, review access logs and repeat the risk assessment yearly. Your safeguards keep up as features, user numbers and threats change over the product's lifetime.

    Planning a Healthcare App That Handles Patient Data?

    Tell us what your app does and who uses it. We'll map the PHI risks and outline the safeguards it needs before you commit budget.

    Technologies We Use for HIPAA Compliant App Development

    Every tool in our stack earns its place by meeting healthcare security requirements. We choose HIPAA-eligible cloud services, identity providers that sign BAAs and HL7 FHIR standards so our HIPAA compliant app development solutions pass audits and scale.
    SwiftSwift
    KotlinKotlin
    React NativeReact Native
    FlutterFlutter

    Who We Build HIPAA Compliant Apps For

    Each healthcare buyer carries different risks. We shape our HIPAA compliant app development solutions around how your organization handles PHI, who your users are and which regulators and partners will review the final product.
    Digital Health Startups

    Digital Health Startups

    We help founders launch HIPAA compliant MVPs that pass hospital security reviews and investor due diligence. You start with the right architecture and avoid a rebuild after your first enterprise deal.
    Telehealth Platforms

    Telehealth Platforms

    We build video visit, messaging and scheduling platforms where every session is encrypted and every vendor in the call stack is covered by a signed BAA before patients log in.
    Mental Health App Companies

    Mental Health App Companies

    Therapy notes and mood data need extra care. We build mental health apps with strict role separation, private messaging and consent controls that keep psychotherapy notes apart from general records.
    Hospital & Health Systems

    Hospital & Health Systems

    We build patient apps and internal tools that connect to your EHR through HL7 and FHIR and follow the security policies your IT and compliance teams already enforce.
    Health Insurance / Payers

    Health Insurance / Payers

    We build member apps and claims tools that show benefits, claim status and care options while keeping PHI locked to the member, the plan and authorized staff.
    Wellness & mHealth Companies

    Wellness & mHealth Companies

    A wellness app that shares data with providers or health plans can fall under HIPAA. We build mHealth apps that handle that shift safely, with secure wearable sync and clinician dashboards.

    Behavioral Health Providers

    Behavioral Health Providers

    We build scheduling, telehealth and records tools for behavioral health practices with tight access rules. Counselors, case managers and billing staff each see only what their role requires.

    Medical Device Companies

    Medical Device Companies

    We build companion apps and cloud backends for connected medical devices. Readings travel encrypted from device to app to clinician, and audit logs record every access along the way.
    What Our Clients Say

    Our behavioral health platform required careful access separation and secure messaging. 8ration built both into the product while keeping the user experience simple and dependable.

    Lukas Schneider

    Technology Director

    8ration gave our patient portal a security-first foundation, with clear PHI workflows, strong access controls, and documentation our compliance team could actually use.

    Lauren Mitchell

    Healthcare Product Director
    quotes

    From discovery through deployment, the team handled our telehealth platform with care. HL7 integration, encryption, and audit logging were planned without slowing development.

    Oliver Bennett

    Telehealth Operations Manager

    FAQs About HIPAA Compliant App Development

    What is hipaa compliant app development?

    +

    A HIPAA compliant app protects the health information it creates, stores or sends according to the HIPAA Privacy, Security and Breach Notification Rules. Building one means encryption, access controls, audit logs, a signed BAA with every vendor and a documented risk assessment, all planned from the first design decision.

    How much does it cost to build a hipaa compliant app?

    +

    Most HIPAA compliant apps we build cost between $30,000 for a focused MVP and $300,000 or more for an enterprise platform. EHR integrations, the number of user roles, the platforms you target and third-party services move the price most. Our app cost calculator gives you a starting estimate.

    How long does hipaa compliant mobile app development take?

    +

    A standard build takes about 18 weeks in our process. Discovery and risk assessment fill the first two weeks, development runs from week 4 to week 16 and testing wraps up by week 18. Large platforms with several EHR integrations can take up to 9 months.

    What is the difference between hipaa-ready and hipaa-compliant?

    +

    HIPAA-ready describes a product or service with the technical features compliance needs, such as encryption and audit logs. HIPAA-compliant describes how your organization runs the app day to day, with signed BAAs, completed risk assessments, trained staff and enforced policies. No vendor can make you compliant on its own.

    Do mobile apps need to be hipaa compliant?

    +

    A mobile app needs HIPAA compliance when it creates, receives, stores or transmits PHI for a covered entity such as a provider or health plan, or for one of their business associates. A consumer fitness app that never shares data with those organizations usually falls outside HIPAA.

    What technical safeguards are required for a hipaa compliant app?

    +

    The HIPAA Security Rule calls for access controls, audit controls, integrity controls, person or entity authentication and transmission security. In practice that means unique user IDs, role-based access, MFA, automatic logoff, encryption at rest and in transit, and tamper-resistant logs of every access to PHI.

    Can react native or flutter apps be hipaa compliant?

    +

    Yes. HIPAA governs how data is handled and says nothing about which framework you use. A React Native or Flutter app can be compliant when it encrypts local storage, avoids caching PHI in plain text, uses certificate pinning and runs on HIPAA-eligible backend services covered by signed BAAs.

    What is a business associate agreement (baa) and why does it matter?

    +

    A Business Associate Agreement is a contract in which a vendor that handles PHI for you agrees to protect it under HIPAA rules. Sharing PHI with a vendor that has not signed one is itself a violation. Cloud hosts, email services, analytics tools and development partners all need one.

    How do you handle phi in development and testing environments?

    +

    We keep real PHI out of development and testing. Our teams work with synthetic or de-identified data sets, and staging environments copy production security settings. If a test needs live data, access is limited, logged and approved by your compliance officer before anyone touches a record.

    What ongoing maintenance does hipaa compliance require after launch?

    +

    Compliance continues after launch. Your app needs security patches, dependency updates, access log reviews, new BAAs when vendors change and a fresh risk assessment at least once a year or after a major change. New features also need a review before release to confirm they handle PHI correctly.

    Delivering Software That Performs Without Limits

    We craft high-performance applications designed for speed, security, and seamless integration. Join us to build dependable systems, improve productivity, and stay competitive in evolving markets.

    Phone